On premises
The whole platform runs inside your data centre, on your hardware, under your change control. Nothing about the deployment requires an outbound connection to us.
Security · how we handle your institution
We build core banking, wallets, agentic AI and banking hardware estates for regulated institutions. That means the security question is not a footnote to the product. It is most of the product. Here is where the data sits, what our systems are permitted to see, who is watching them run, and exactly what we are certified for.
Where the software sitsIllustrative
On premises, private cloud or regional residency. Your choice, not ours.
01 · Data handling
Every product on this site, whether Fahim AI, MBuke or the GRGBanking hardware estate, is delivered in one of three shapes. The decision belongs to your risk committee and your regulator, and we build to it rather than around it.
The whole platform runs inside your data centre, on your hardware, under your change control. Nothing about the deployment requires an outbound connection to us.
Hosted infrastructure in the region you nominate, sized to the book you actually have and scaled ahead of the events you can predict, such as salary runs, month end and campaign launches.
Where records physically live is written into the engagement before the first environment is built, not discovered at the audit. You nominate the region, and our teams operate in it.
Migrations run against your data in your environment. Where a copy is unavoidable, a rehearsal for a core migration for instance, it is scoped, time limited and destroyed on a date agreed in writing.
02 · Privacy
Agentic AI and a wallet platform both work by being trusted with something. These are the three rules that trust is built on, and they hold whether the deployment is ours to operate or yours.
Access is scoped to the task
An agent that reconciles a suspense account is given the suspense account, not the ledger. Our engineers get named, time limited access to the environments they are working in, granted through your access control and revoked by it.
Never pooled across institutions
The fraud, risk and personalization models we build are fitted to your data and belong to your institution. Nothing from one customer’s book is used to improve another customer’s model, and nothing is fed back into a general purpose model.
Reviewable after the fact
Agentic AI is only acceptable in a bank if the work it completed can be reconstructed. Fahim writes what it did, what it read and what it changed, into an audit trail your own people can read without asking us.
03 · Platform reliability
Availability is part of security. The platforms underneath a bank fail at times nobody is rostered for, so someone is always watching them run. This is what that watching consists of.
A failed end of day posting run is a bank that cannot open. On managed T24 the batch is attended, not discovered in the morning.
Payout capacity is scaled ahead of a salary run rather than after the complaints, and comes back down when the peak passes.
Every terminal, recycler and smart teller machine verified and reported, so a branch starts the day knowing what it has.
A contained intrusion attempt produces a report before anyone arrives at their desk. You hear it from us first.
Availability targets, recovery objectives and escalation paths are agreed per engagement and written into the contract. We do not publish a headline uptime figure here, because a number nobody has signed is not a commitment.
04 · Compliance posture
Regulated institutions in Saudi Arabia and the UAE answer to their own supervisors, and our job is to make that answer easier to give, not to imply we have already given it for you.
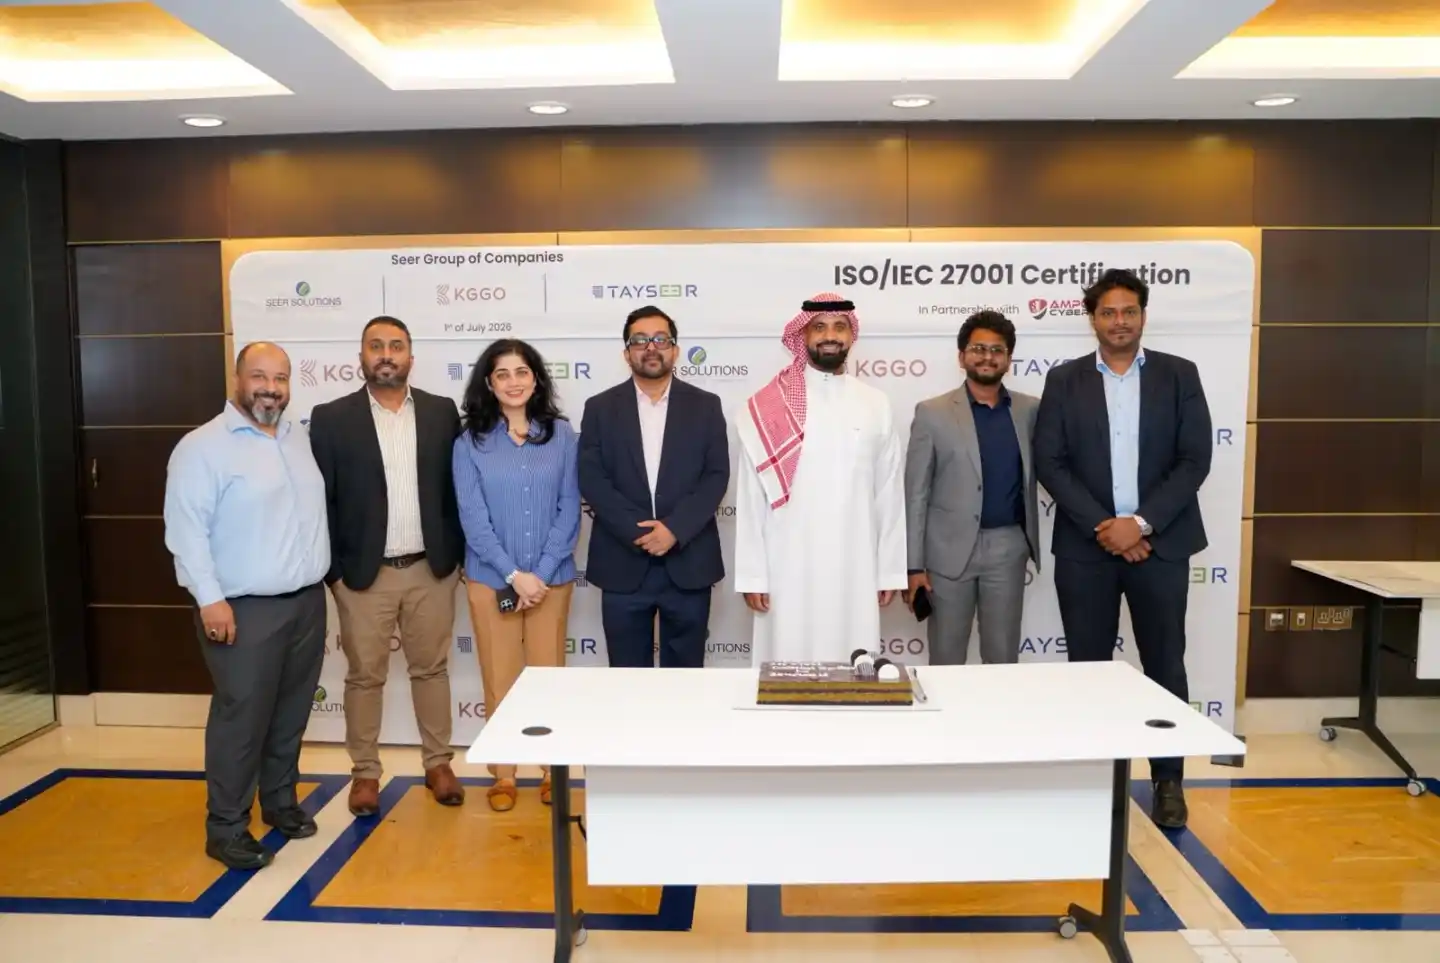
What we holdVerifiable
What we do not claimOn the record
Security enquiries
Most institutions arrive here with a vendor assessment, a data residency requirement or a regulator’s question already in hand. Send it. You will get a straight answer, including where the answer is no.
601, One Lake Plaza, Cluster T, JLT, DubaiOffice 7, 2nd Floor, Selam Building, Al Rawabi, Riyadh
One inbox, answered by the team that builds the software.